Five-step walkthrough
Walkthrough: CI/CD pipeline with gates that block and a recorded rollback
Five screenshots in the order I would talk through them. Each step names what to look at, and every chip and Prev/Next link is a real URL fragment.
Step 1 of 5
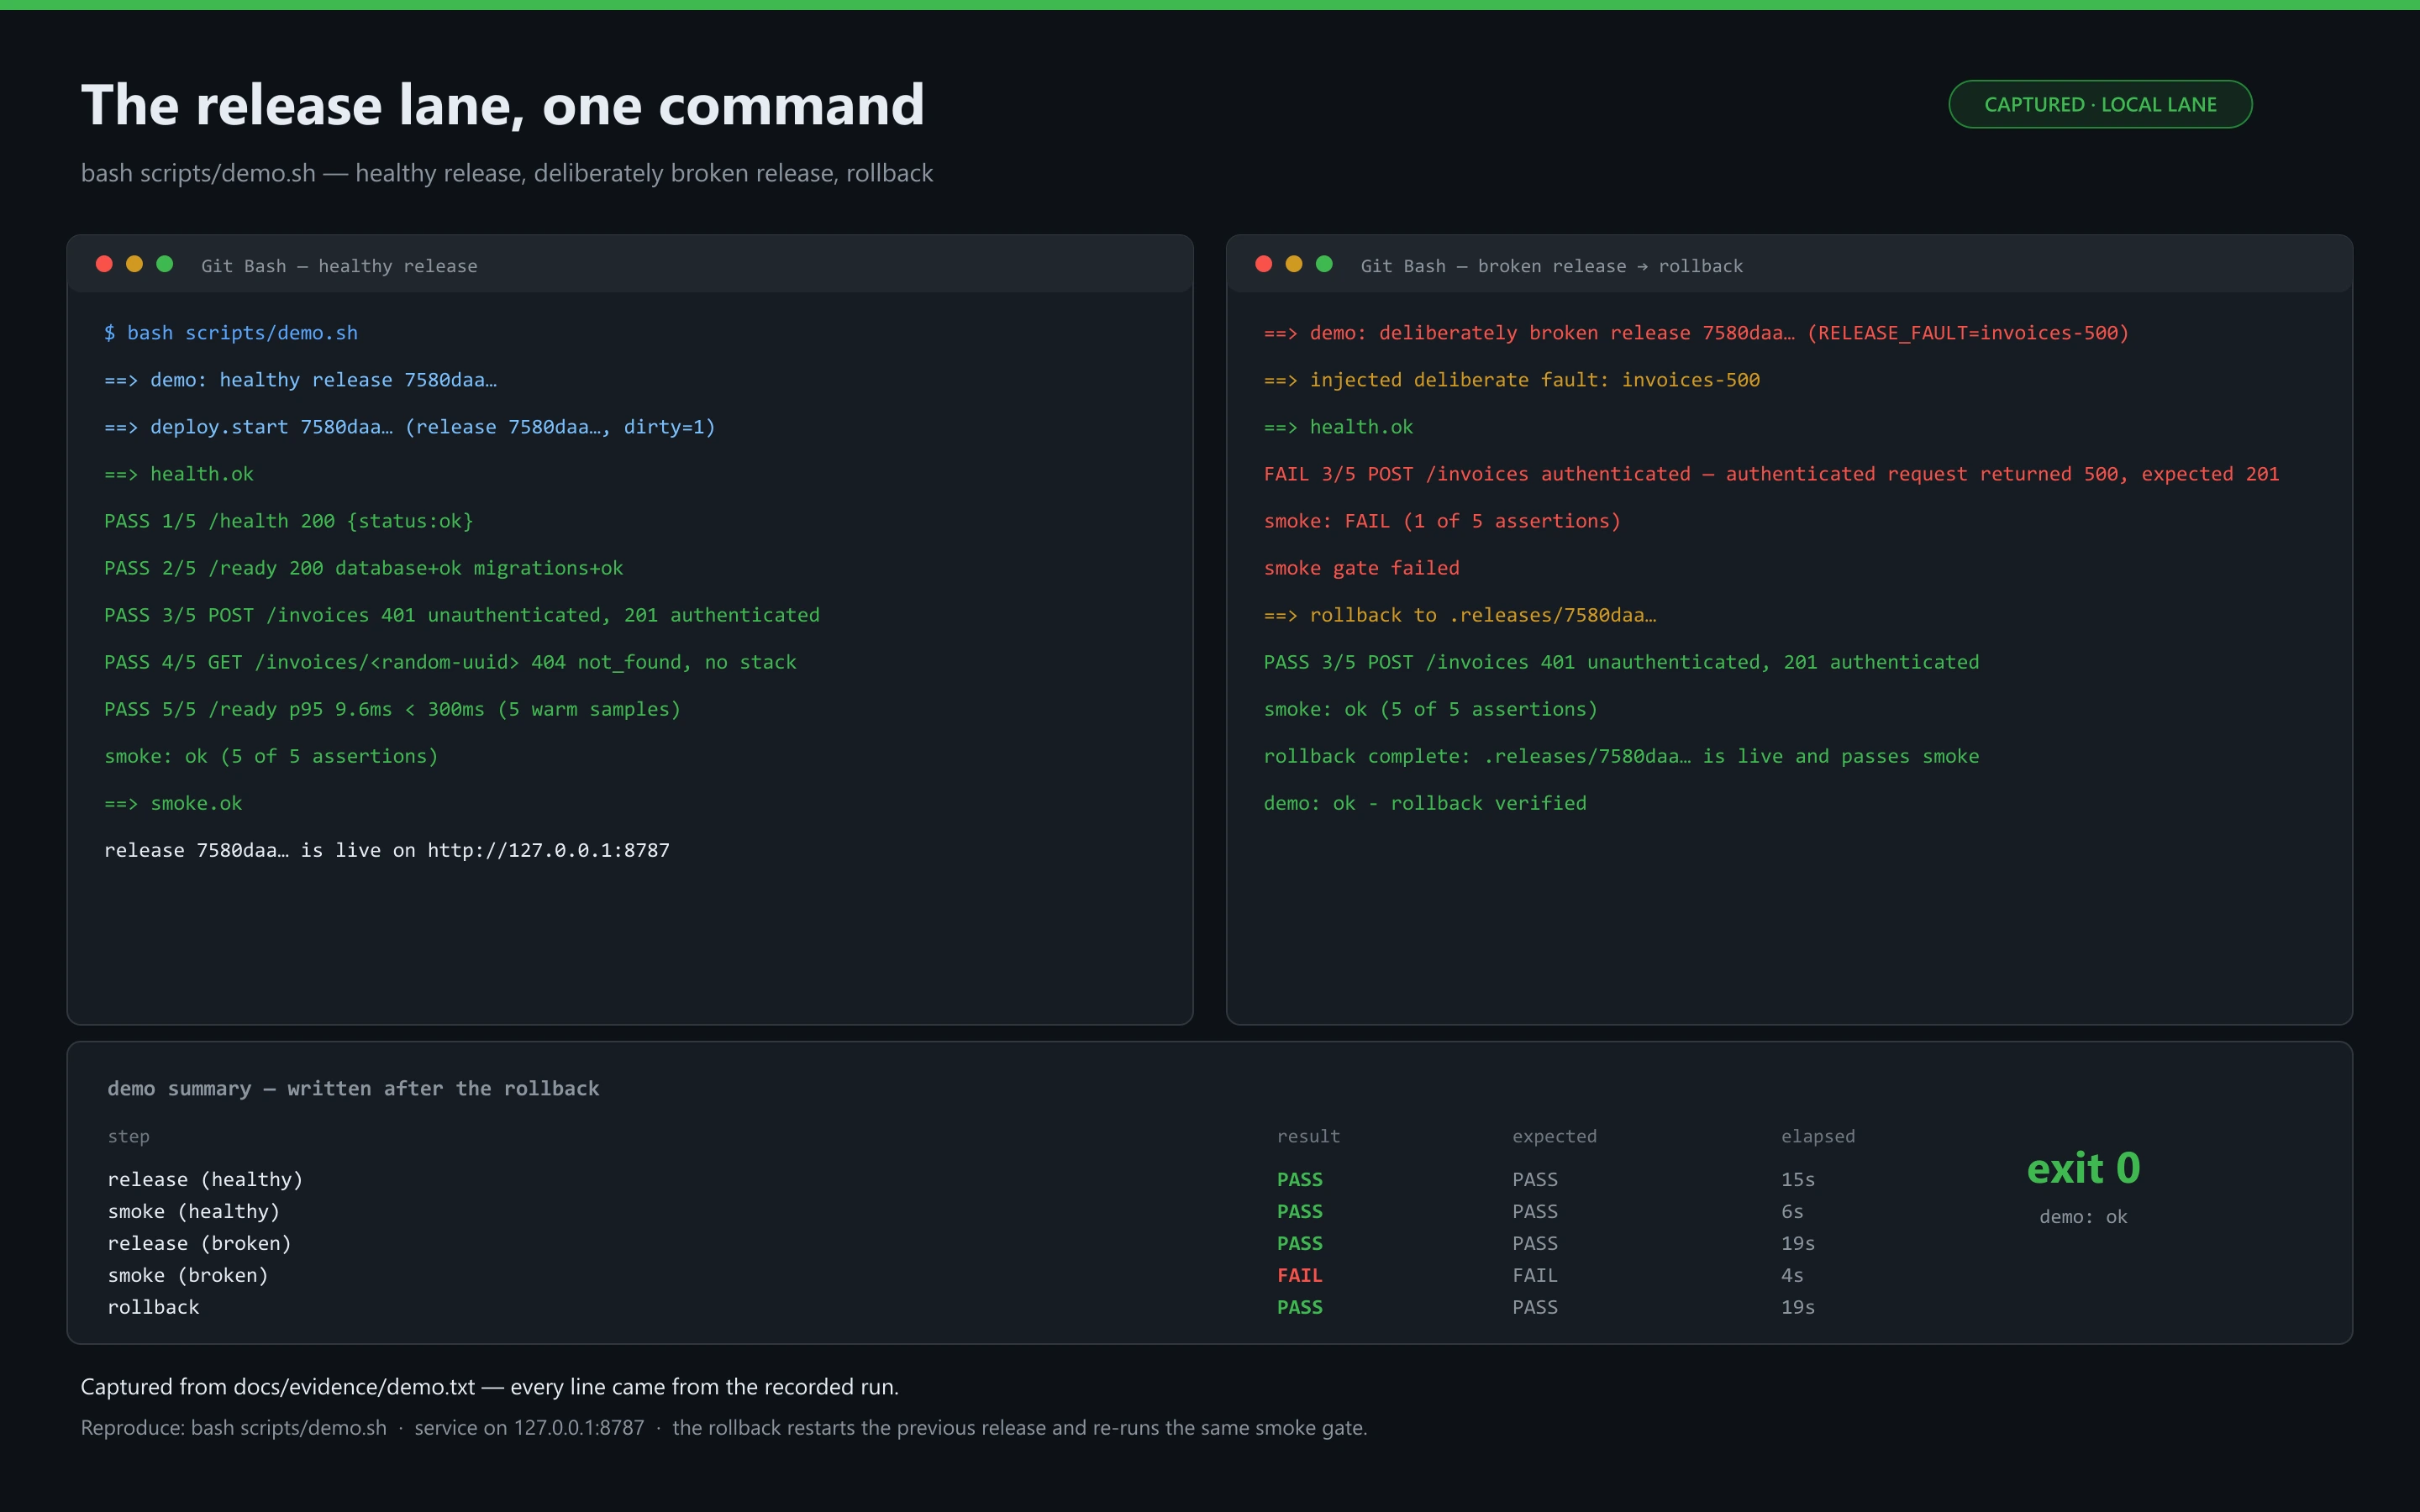
One command, two releases
The left pane is a recorded healthy release: five smoke assertions pass and the process serves on port 8787. The right pane is a deliberately broken release whose invoice request returns 500, so three of five assertions miss and the script rolls back.
Step 2 of 5
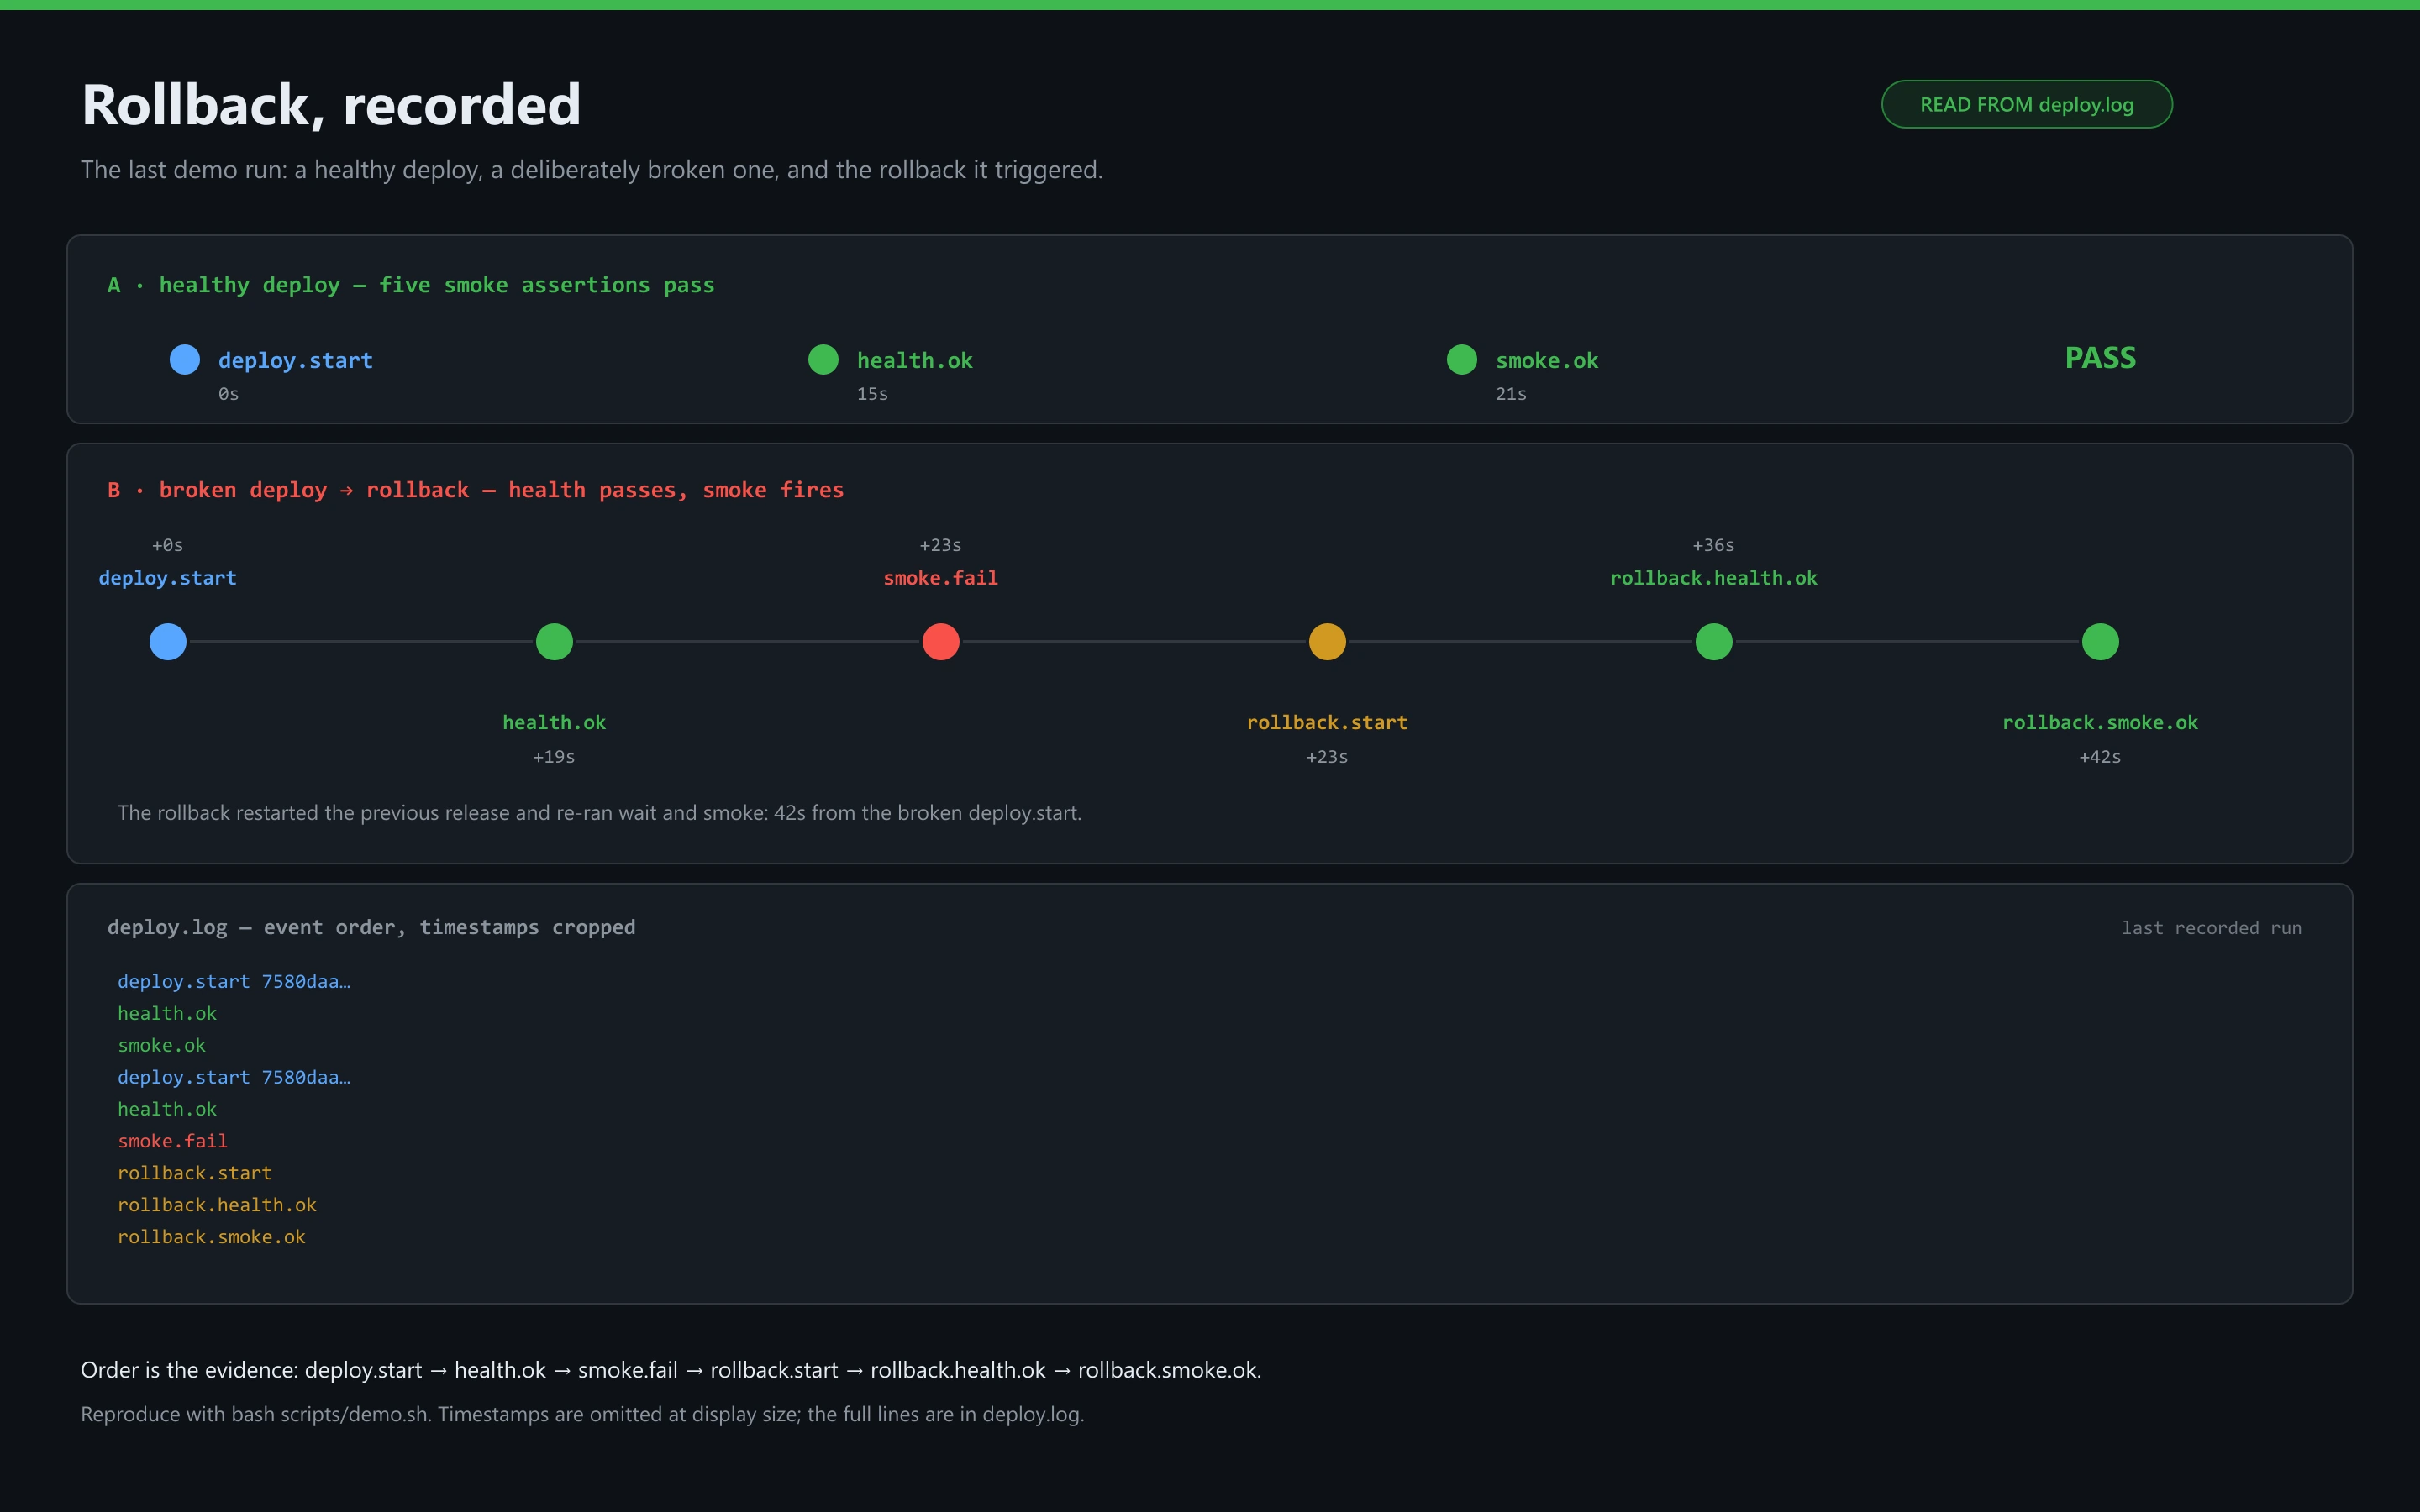
The rollback timeline, second by second
Lane A shows the healthy deploy moving from deploy.start to health.ok and smoke.ok. Lane B records smoke.fail and rollback.start at 23 seconds into the run, rollback.health.ok at 30 seconds and rollback.smoke.ok at 42 seconds.
Step 3 of 5
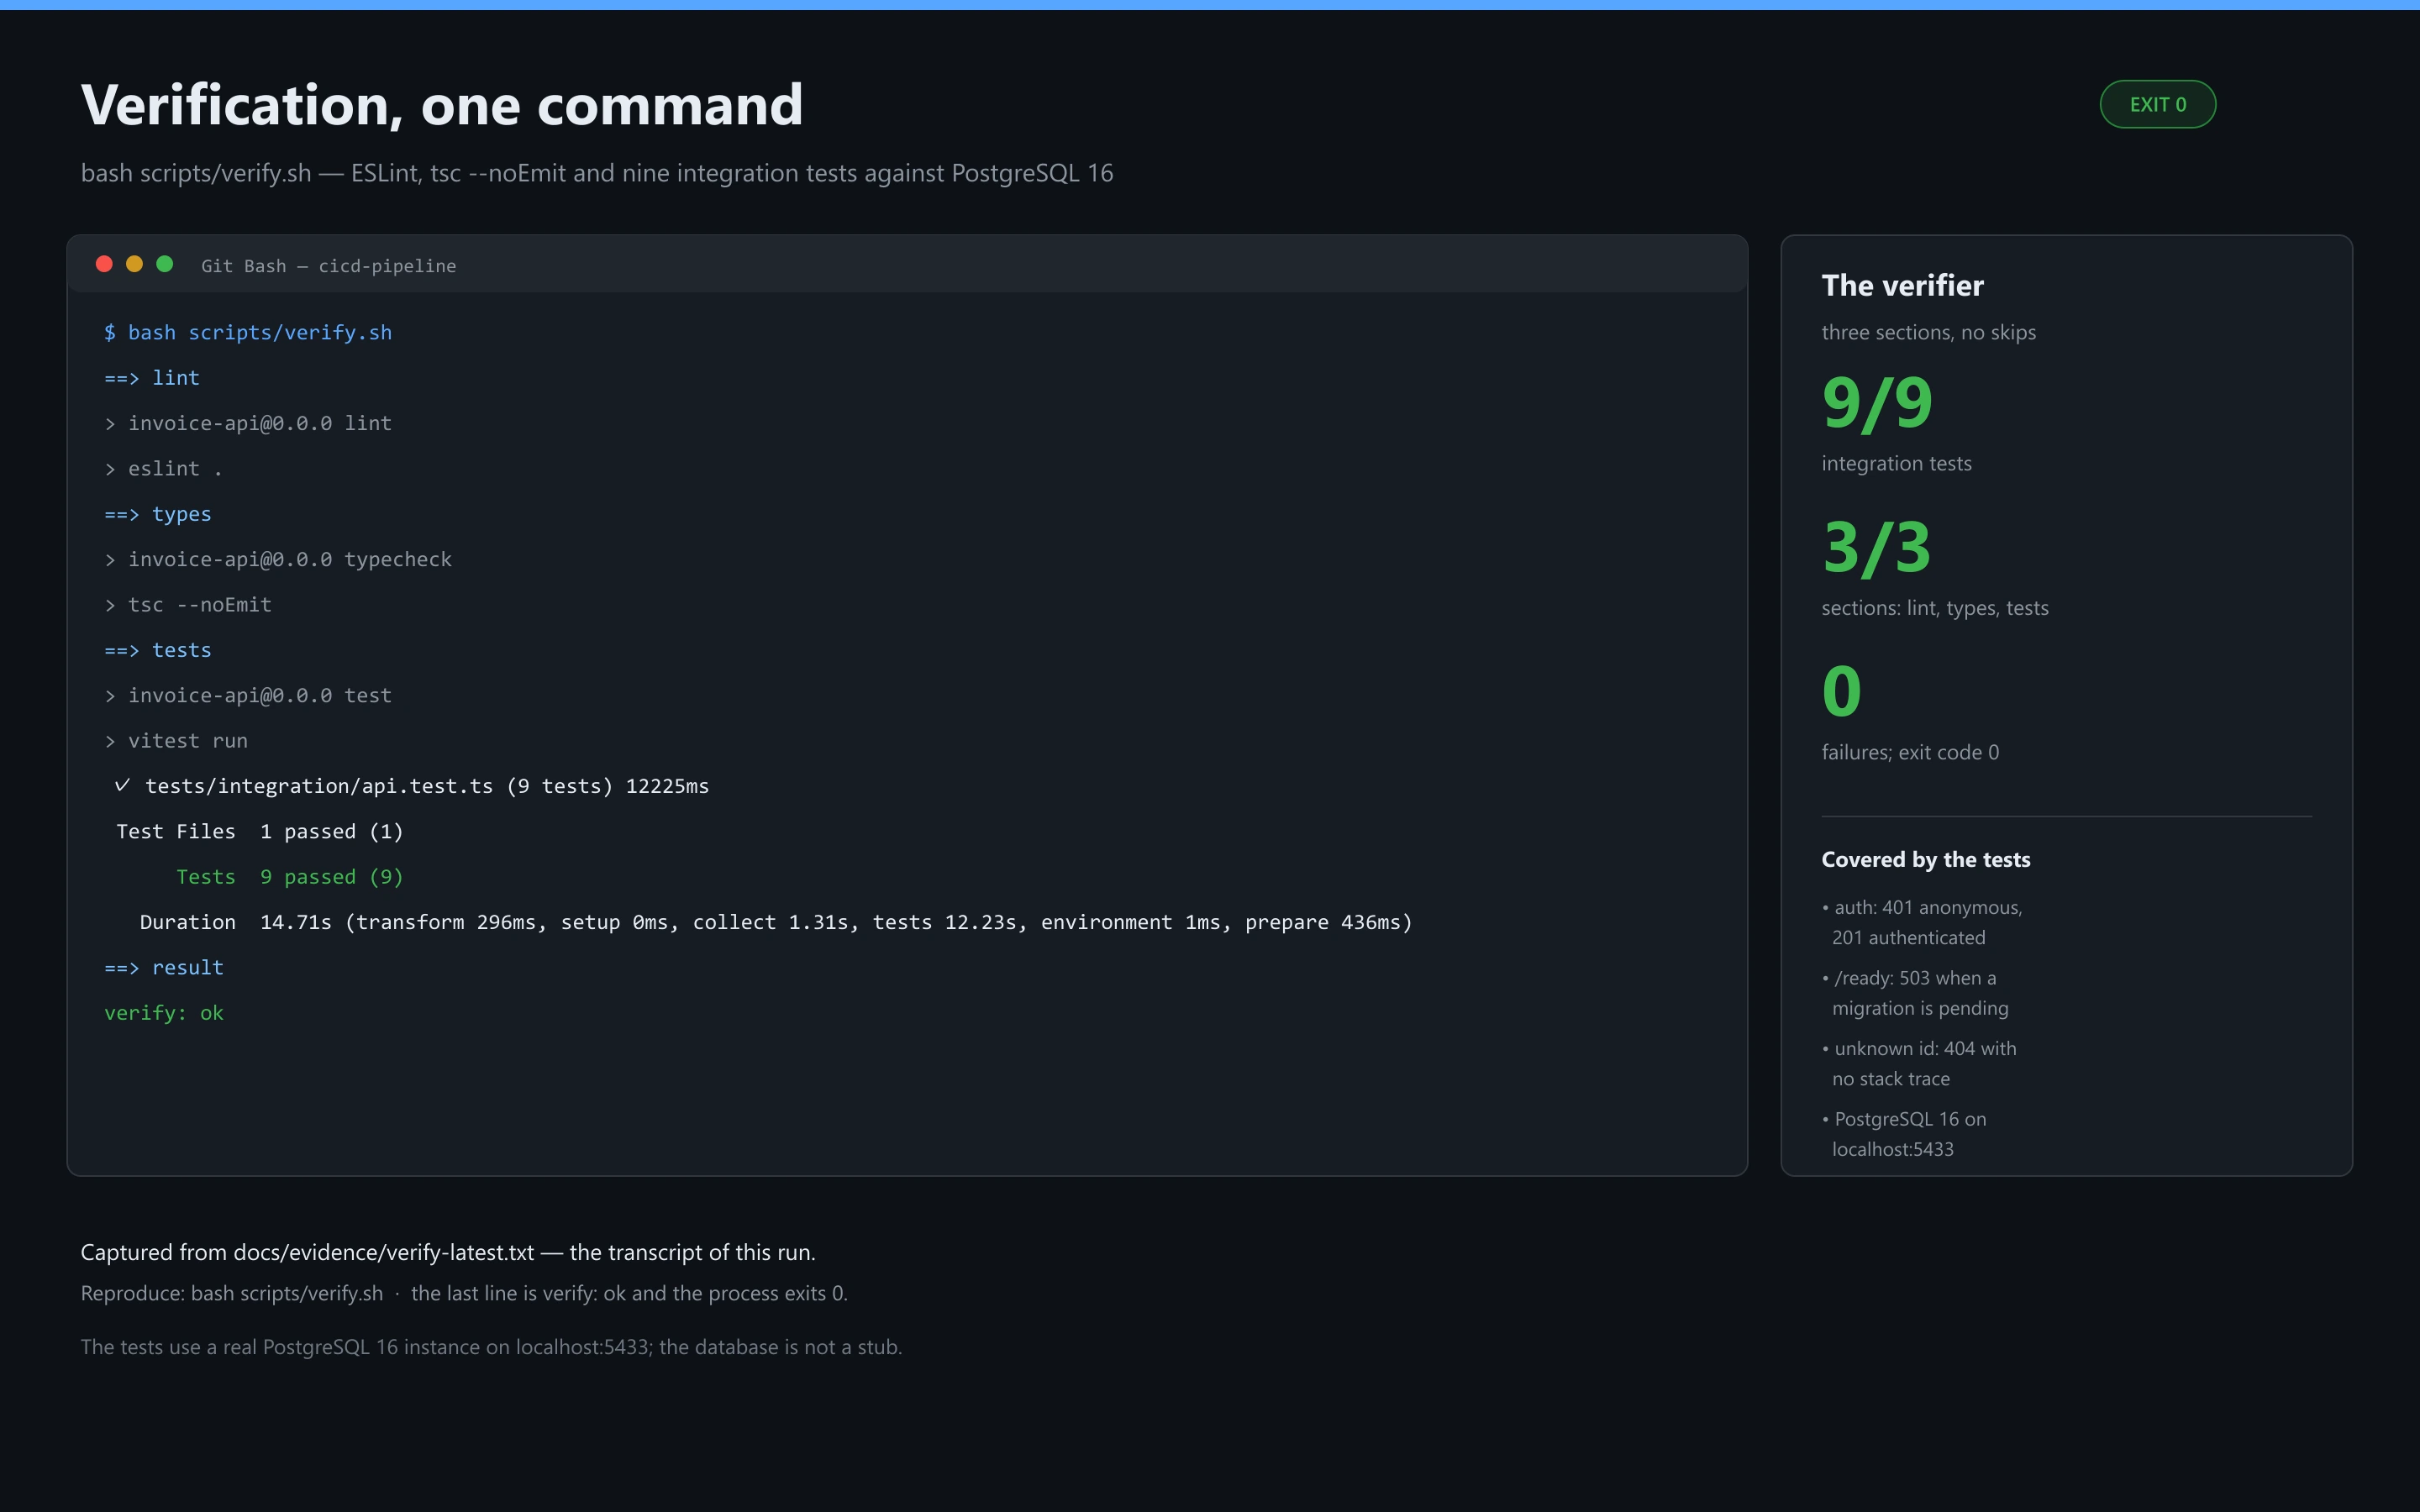
Verification runs lint, types and tests
The transcript runs ESLint, tsc --noEmit and nine integration tests against PostgreSQL 16 in 14.71 seconds. Three sections report 9/9 tests, 3/3 sections and zero failures, and the last line is verify: ok.
Step 4 of 5
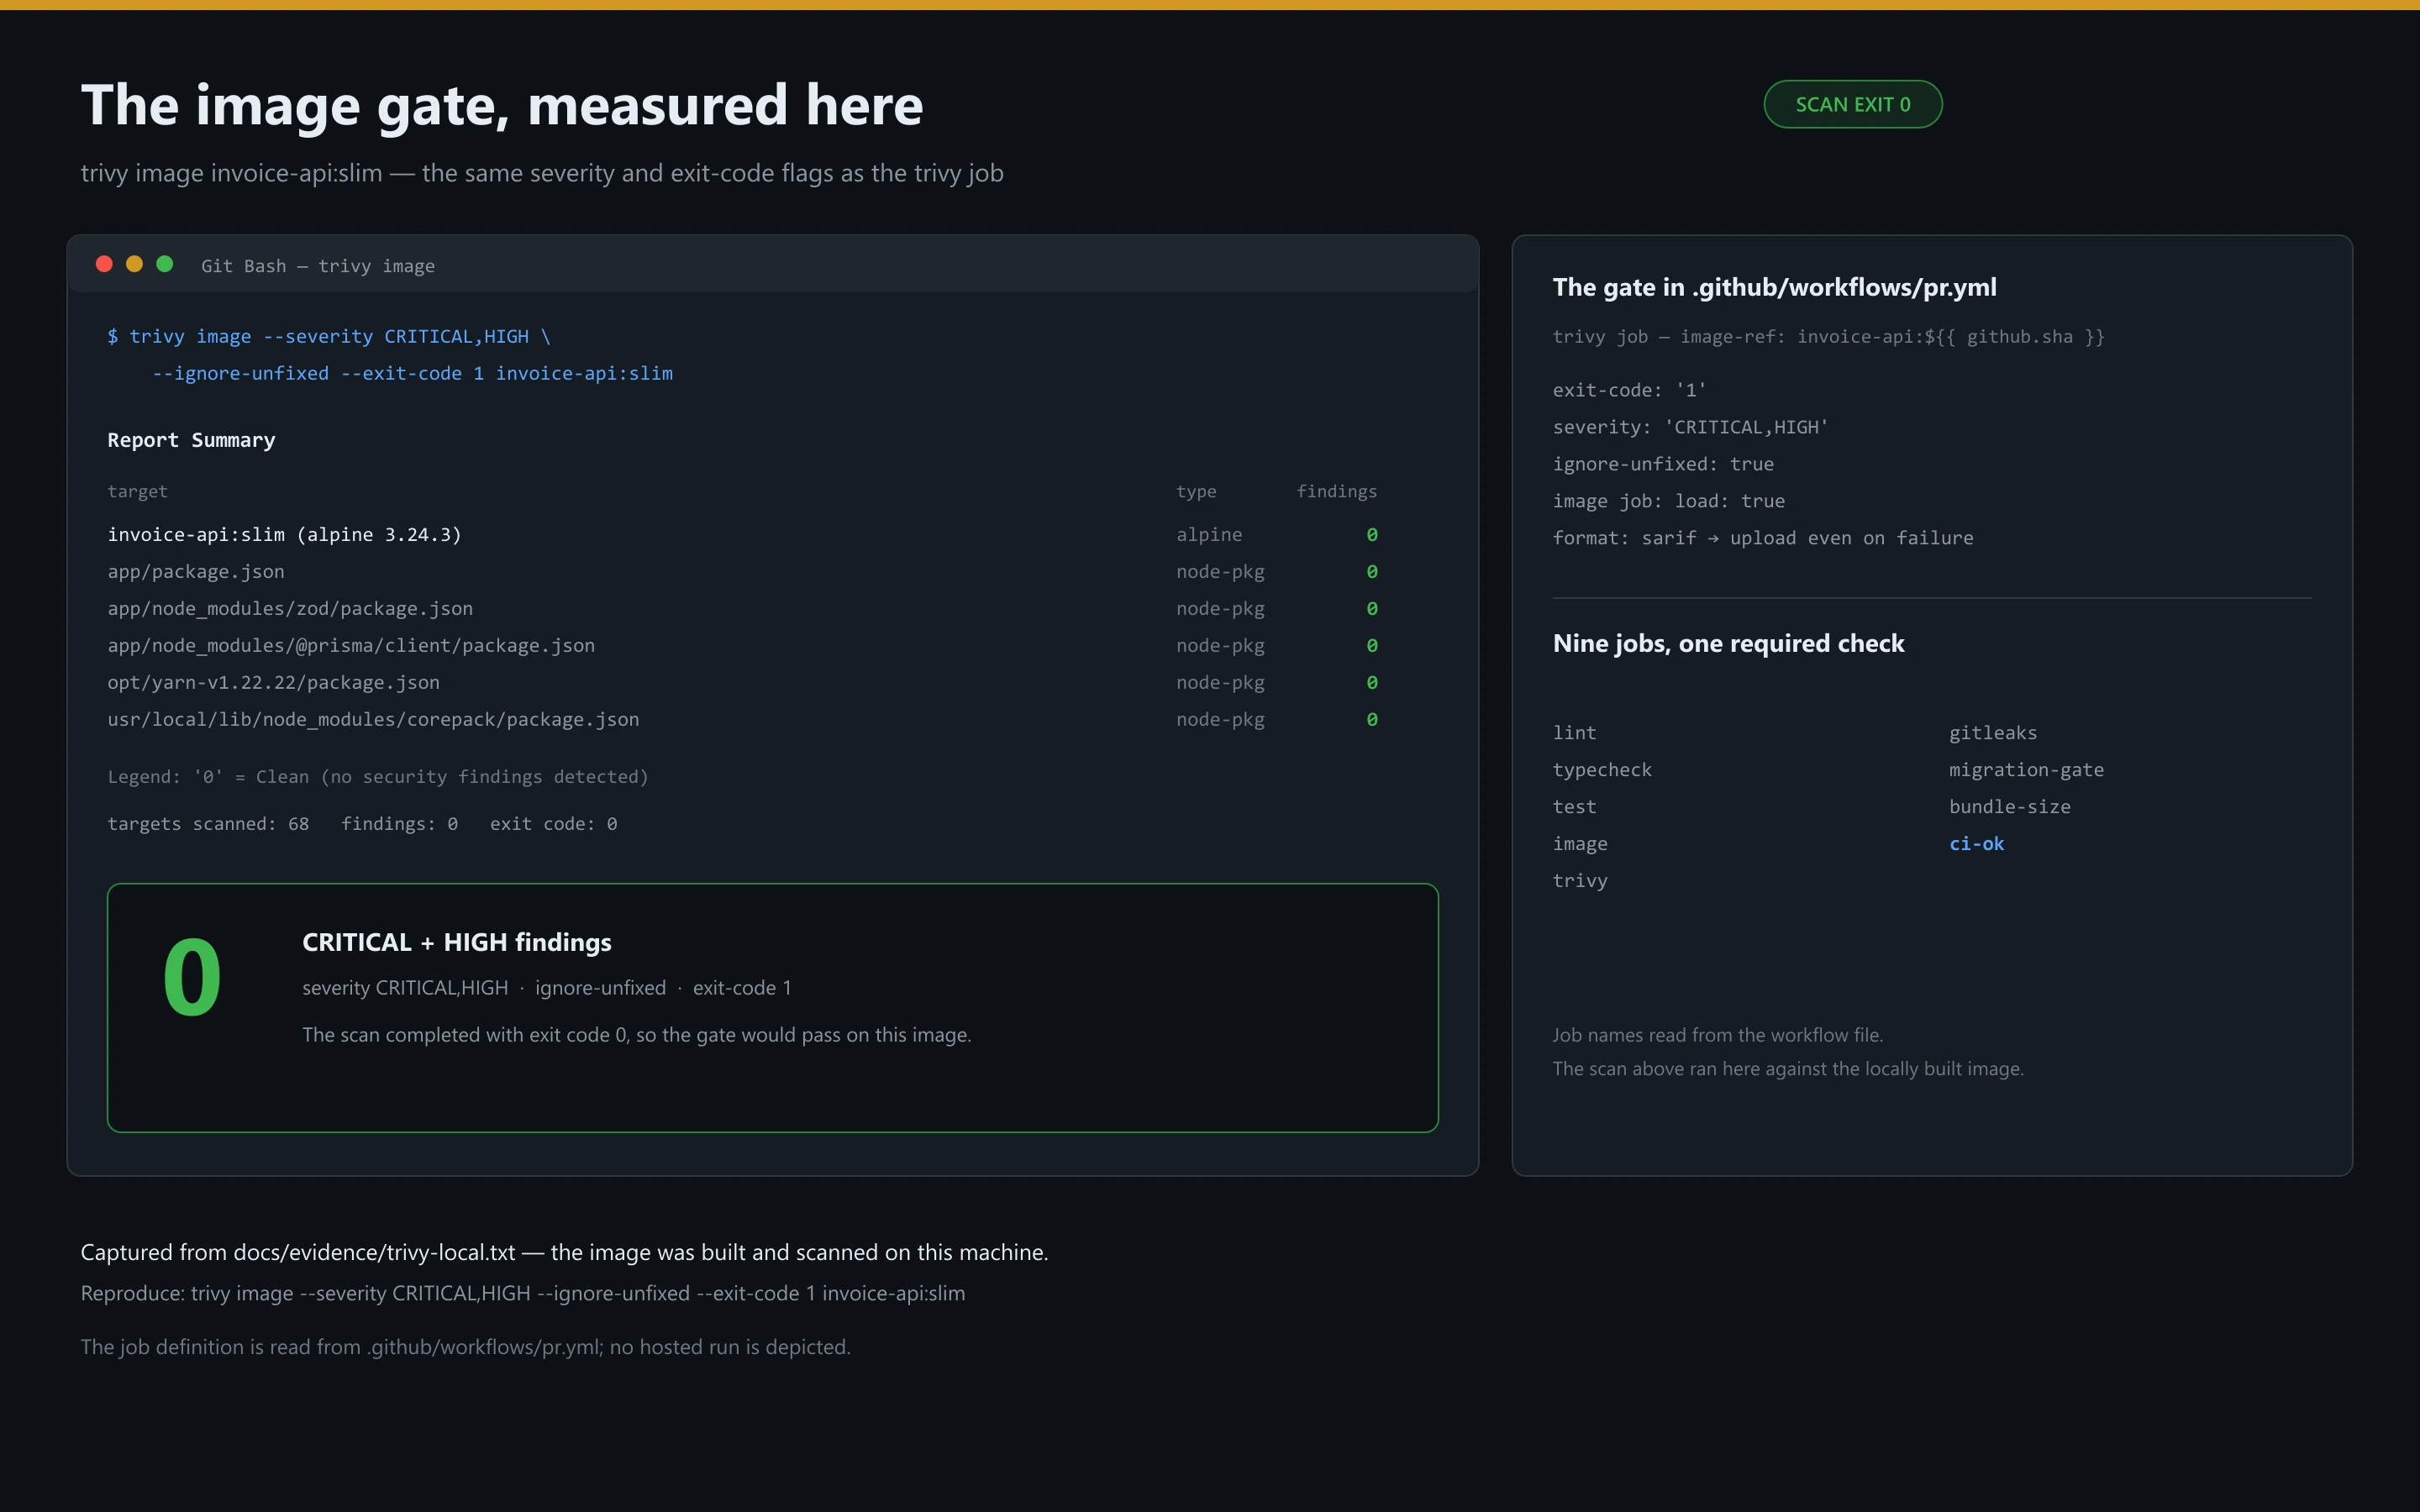
The image gate, measured here
The Trivy run scans 68 targets in invoice-api:slim at CRITICAL and HIGH with ignore-unfixed and reports zero findings at exit 0. The right panel reads the same flags from the trivy job in pr.yml, beside the nine jobs and the one required ci-ok check.
Step 5 of 5
The summary line closes the loop
The table at the bottom of the transcript records five rows: the healthy release and smoke pass, the broken release's smoke row reads FAIL, and the rollback passes. The run ends with exit 0 and demo: ok, so the file records the order the release lane followed.